Protected: Analysis of the BlackBasta infrastructure: Cobalt Strike
There is no excerpt because this is a protected post.
Blog · research & analysis
There is no excerpt because this is a protected post.
UPDATES: 27.11.2024: As mentioned by TrustWave, “Supercar Phishing Kit” has an high level of overlapping with the most recent update of “Rockstar 2FA Phishing-as-a-Service” 26.09.2024: As mentioned by Any.Run, “Supercar Nebula” has an high level of overlapping with “Storm-1575“ In August 2024, Fortgale identified and analyzed an extensive phishing campaign employing a previously publicy undocumented … Read more
In the evolving landscape of cybersecurity threats, Fortgale is tracking PhishSurf Nebula, an advanced Cyber Espionage group active since 2021 and primarily targeting entities within the Banking & Finance and Real Estate sectors across Europe and North America. In particular, most of the involved companies are Private Equity Firms, Hedge Funds, Venture Capitals and Luxury … Read more
Fortgale has been tracking an Italian Threat Actor, internally dubbed as Nebula Broker, since March 2022. The actor uses self-made malware (BrokerLoader) to compromise Italian systems. Further analysis revealed that the attacker has been operating since the end of 2020. Although this threat is not well-known, the number of compromises is particularly extensive. Indeed, Fortgale … Read more
In the ever-evolving landscape of cyber threats, threat actors are constantly seeking new and innovative ways to deceive and compromise unsuspecting targets. One of the latest techniques that Fortgale observed gaining prominence over the last few months is the utilization of QR codes in phishing email campaigns (Spearphishing Technique – T1566). In this article, we … Read more
Risks and Solutions How to protect and how to react The identification of this type of compromise can occur on different levels: Fortgale recommends performing proactive threat hunting activities to identify this type of compromise potentially undetected by the systems mentioned above. Choose the solution that best fit your company
Over the last week (26th of July 2021), CERT-AGID observed a malspam campaign whose intent was to spread the FickerStealer malware via the Hancitor loader to steal the credentials present on the victim’s machine. The emails, themed “Pagamenti“, contained an attached Word or Excel document, within which macros were recorded for downloading and executing the … Read more
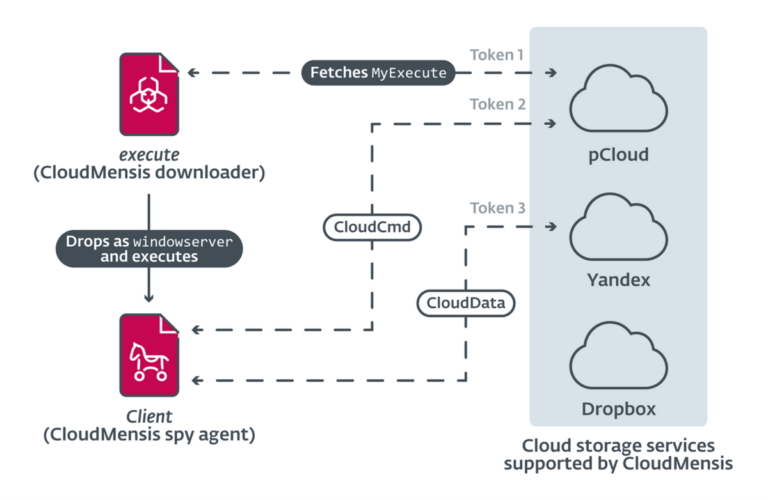
A new backdoor for MacOS systems has been discovered in recent days by ESET researchers. The goal of the malware is to exfiltrate information from the victim system by exploiting cloud storage services.The Backdoor, named by CloudMensis researchers, recovers information such as documents, email messages and attachments, files on removable devices, screenshots and the sequence … Read more
In May 2022, a new, particularly evasive Worm was observed for the first time, spreading in private and corporate networks through compromised USB sticks.This new Worm has been given the name “Raspberry Robin“. Worms that propagate through USB devices are certainly not new threats and very often, since they are old malware, command and control … Read more