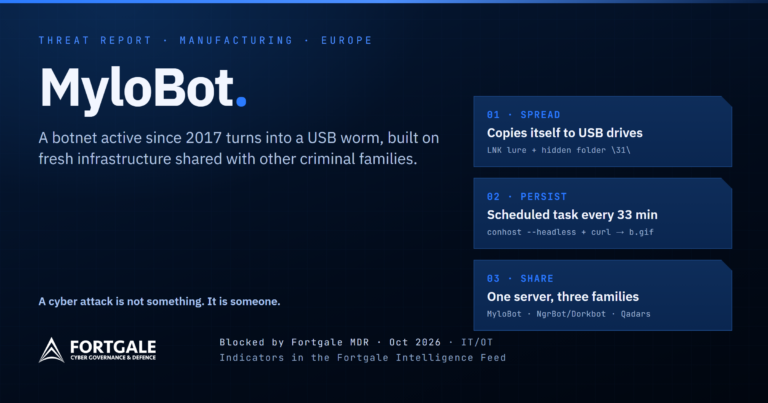
MyloBot goes USB: the botnet that crawls towards the production line
Fortgale MDR stopped a new MyloBot variant at a European manufacturing company: the botnet now spreads as a USB worm, on fresh infrastructure shared with NgrBot/Dorkbot and Qadars.
Tag
Fortgale MDR stopped a new MyloBot variant at a European manufacturing company: the botnet now spreads as a USB worm, on fresh infrastructure shared with NgrBot/Dorkbot and Qadars.
In recent weeks, consistent with previously documented activity (background), we have observed a general increase in compromise activity across monitored environments. Criminal groups deploy malware for multiple objectives: Ransomware execution, sensitive data exfiltration, and credential harvesting. Qakbot — documented in detail under MITRE ATT&CK S0650 — is consistently used for all three. Unlike previous campaigns, … Read more
Emotet malspam wave of 23 September 2020: three distinct delivery patterns, document macro chain, payload deployment and host-level indicators.
Campagna malware Emotet (Trojan Bancario), che ha targettizzato utenti italiani di rientro dalle ferie estive. Info sul Malware Emotet ” While Emotet historically was a banking malware organized in a botnet, nowadays Emotet is mostly seen as infrastructure as a service for content delivery. For example, since mid 2018 it is used by Trickbot for … Read more
Indicators of Compromise from August-September 2018 banking-malware campaigns (Emotet, TrickBot) targeting Italian infrastructures.