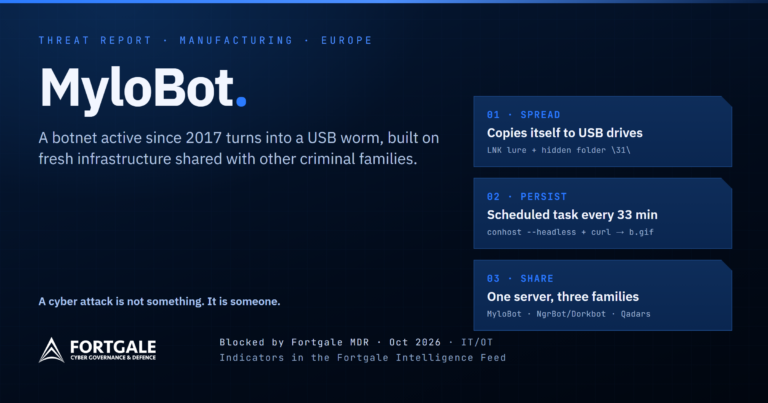
MyloBot goes USB: the botnet that crawls towards the production line
Fortgale MDR stopped a new MyloBot variant at a European manufacturing company: the botnet now spreads as a USB worm, on fresh infrastructure shared with NgrBot/Dorkbot and Qadars.
Category
Fortgale MDR stopped a new MyloBot variant at a European manufacturing company: the botnet now spreads as a USB worm, on fresh infrastructure shared with NgrBot/Dorkbot and Qadars.
On 4 September 2026 at 22:20 UTC, an unauthenticated request began landing on Magento and Adobe Commerce storefronts and walking straight to remote code execution. No login. No admin session. No plugin. The flaw, tracked as CVE-2026-75650 and named StyleSmuggler, carries a CVSS of 10.0, and it was exploited in the wild for roughly three … Read more
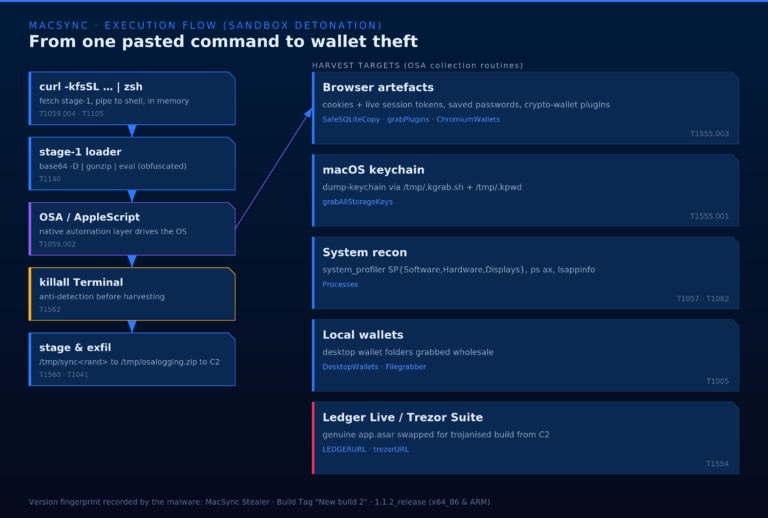
No exploit. No attachment. No phishing email. In this campaign the threat actor needs the victim to do exactly one thing: copy a command from an installation guide and paste it into the macOS Terminal. In the summer of 2026 our SOC intercepted that moment three times, on the same corporate endpoint, and blocked it three times. The target: a developer’s Mac. The payload: MacSync, an infostealer sold as Malware-as-a-Service and built for the Apple ecosystem
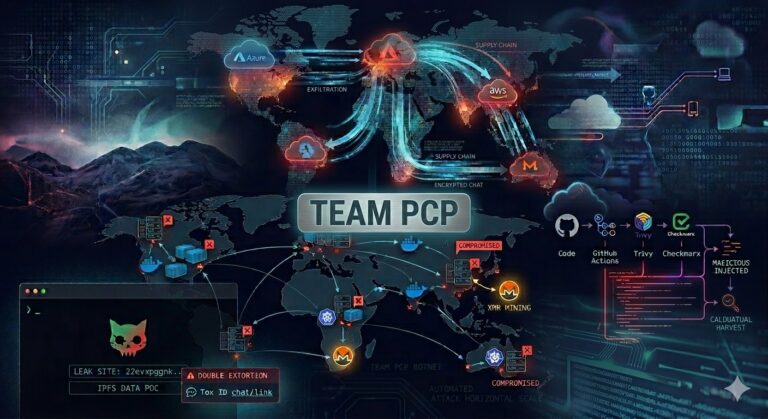
TeamPCP: The Rise of Cloud-Native Extortion and Supply Chain Attacks TeamPCP is an emerging cybercriminal collective that became active in late 2025, distinguishing itself through a specialized focus on massive attacks against cloud-native infrastructures. Unlike traditional Advanced Persistent Threat (APT) groups that often prioritize deep persistence on specific endpoints, TeamPCP utilizes high-level automation to scale … Read more
UPDATES: 27.11.2024: As mentioned by TrustWave, “Supercar Phishing Kit” has an high level of overlapping with the most recent update of “Rockstar 2FA Phishing-as-a-Service” 26.09.2024: As mentioned by Any.Run, “Supercar Nebula” has an high level of overlapping with “Storm-1575“ In August 2024, Fortgale identified and analyzed an extensive phishing campaign employing a previously publicy undocumented … Read more
Risks and Solutions How to protect and how to react The identification of this type of compromise can occur on different levels: Fortgale recommends performing proactive threat hunting activities to identify this type of compromise potentially undetected by the systems mentioned above. Choose the solution that best fit your company
Over the last week (26th of July 2021), CERT-AGID observed a malspam campaign whose intent was to spread the FickerStealer malware via the Hancitor loader to steal the credentials present on the victim’s machine. The emails, themed “Pagamenti“, contained an attached Word or Excel document, within which macros were recorded for downloading and executing the … Read more
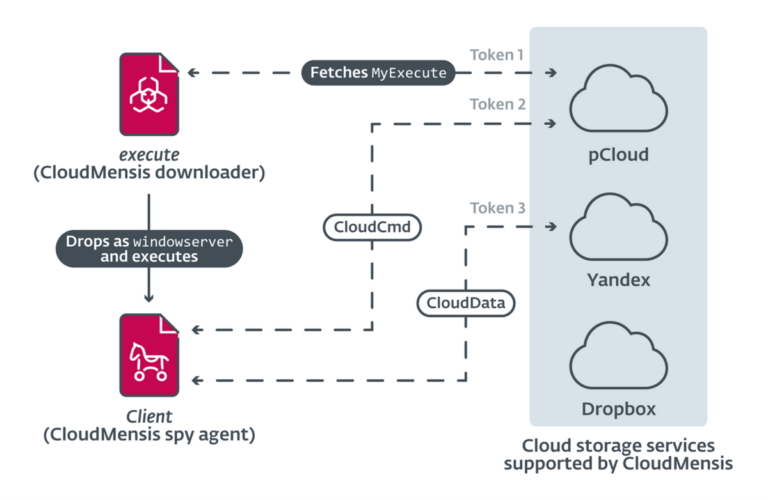
A new backdoor for MacOS systems has been discovered in recent days by ESET researchers. The goal of the malware is to exfiltrate information from the victim system by exploiting cloud storage services.The Backdoor, named by CloudMensis researchers, recovers information such as documents, email messages and attachments, files on removable devices, screenshots and the sequence … Read more
Come ogni secondo Martedì del mese, Microsoft ha rilasciato una serie di aggiornamenti (patch) di sicurezza per i propri sistemi operativi.
In questo mese sono state rilasciate 117 patch per altrettante vulnerabilità, di queste: