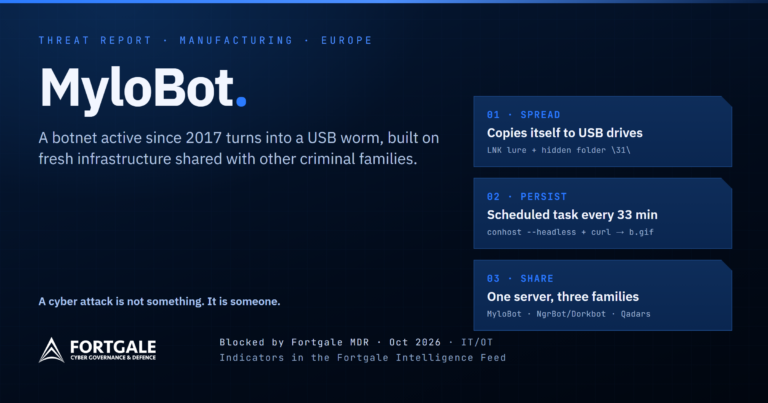
MyloBot goes USB: the botnet that crawls towards the production line
Fortgale MDR stopped a new MyloBot variant at a European manufacturing company: the botnet now spreads as a USB worm, on fresh infrastructure shared with NgrBot/Dorkbot and Qadars.
Tag
Fortgale MDR stopped a new MyloBot variant at a European manufacturing company: the botnet now spreads as a USB worm, on fresh infrastructure shared with NgrBot/Dorkbot and Qadars.
An Italian malspam campaign has been identified with the objective of delivering TrickBot malware via an Excel attachment. The malware has been traced back to the sat1 botnet. TrickBot is a banking trojan developed to steal login credentials for victims’ banking sites through the use of webinjects. Since June 2018, TrickBot has been upgraded with … Read more
Ursnif/Cutwail malspam infrastructure update for June 2021: botnet-driven distribution, lure rotation and host indicators across affected estates.
Italian IoT devices conscripted into botnets and used as launch pads for cyber attacks: device profiles, exposure metrics and remediation considerations.
Insights from FortPot honeynet sensors: scanning waves, exploitation attempts on exposed services, automated brute-force trends and ASN-level intelligence.
