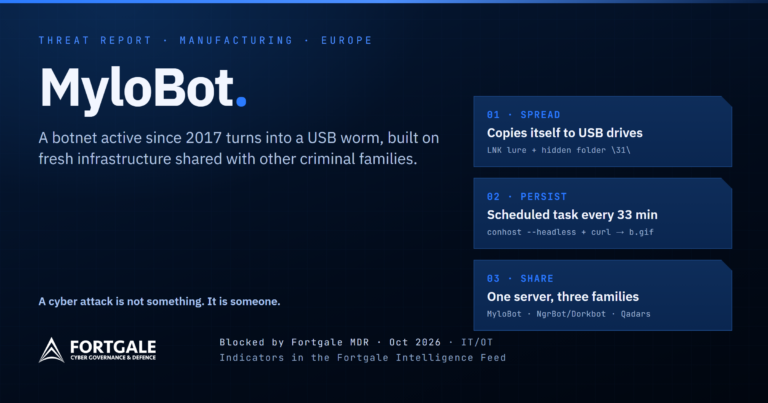
MyloBot goes USB: the botnet that crawls towards the production line
Fortgale MDR stopped a new MyloBot variant at a European manufacturing company: the botnet now spreads as a USB worm, on fresh infrastructure shared with NgrBot/Dorkbot and Qadars.
Category
Fortgale MDR stopped a new MyloBot variant at a European manufacturing company: the botnet now spreads as a USB worm, on fresh infrastructure shared with NgrBot/Dorkbot and Qadars.
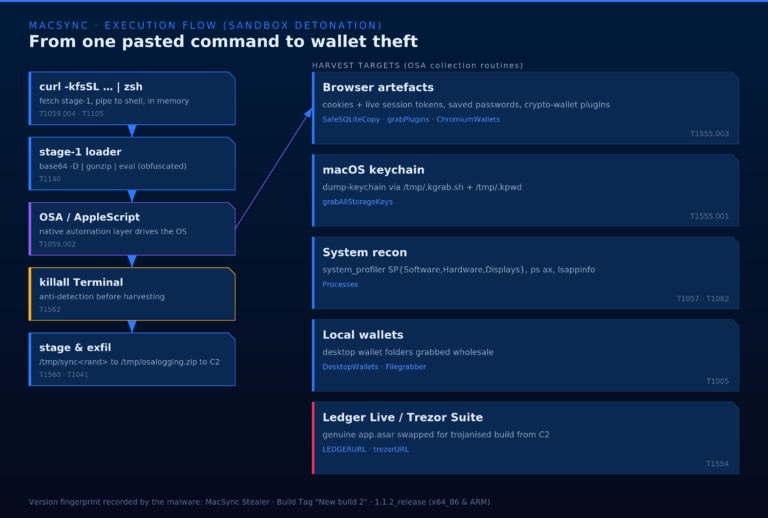
No exploit. No attachment. No phishing email. In this campaign the threat actor needs the victim to do exactly one thing: copy a command from an installation guide and paste it into the macOS Terminal. In the summer of 2026 our SOC intercepted that moment three times, on the same corporate endpoint, and blocked it three times. The target: a developer’s Mac. The payload: MacSync, an infostealer sold as Malware-as-a-Service and built for the Apple ecosystem
On January 24, 2023, Fortgale identified an Agent Tesla malware campaign being delivered via email to compromise the systems of Italian companies. In this technical article, we will analyze the behavior of the malware and how it compromised its victims through the analysis of code characteristics and collected data. It has now become common practice … Read more
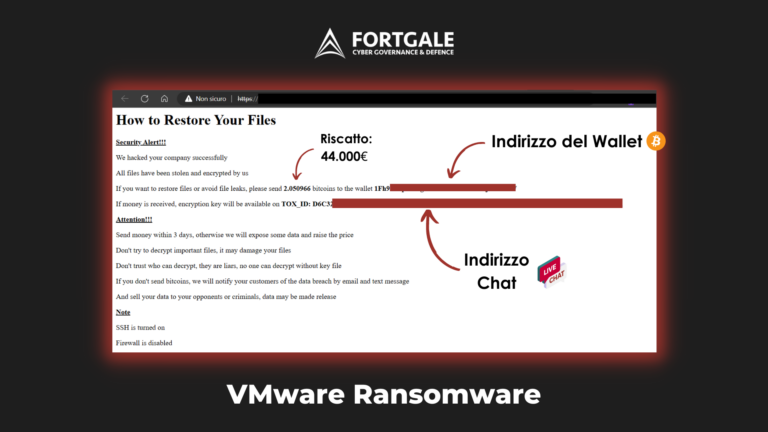
VMware ESXi #Ransomware: What is going on? What does the following code means? D6C324719AD0AA50A54E4F8DED8E8220D8698DD67B218B5429466C40E7F72657C015D86C7E4A In the last few hours, several sources have reported massive Ransomware-type activity against VMware ESXi servers exposed on a public network. The activity currently appears to be conducted by at least 2 different criminal groups. How? Both groups are exploiting a … Read more
After recent online publications regarding the TrueBot malware (VMware, Bleeping and THN), we have decided to contributing with our analysis of this potential new threat. At the end, you will find the indicators of compromise and a Yara rule to identify it. Before starting with the technical analysis of the malware, we believe it is … Read more
Fortgale has identified an offensive campaign targeting Italian business systems, carried out via malicious email containing the StrelaStealer malware. During the compromise, several techniques are observed including: Its purpose is usually to collect information about Outlook and ThunderBird accounts, as also confirmed by our technical analysis. The attention of these Threat Actors is focusing on … Read more