Skip to content

Archive

Month: September 2023

·Emerging Threats

Cyber Attack Risk: Follina

Risks and Solutions How to protect and how to react The identification of this type of compromise can occur on different levels: Fortgale recommends performing proactive threat hunting activities to identify this type of compromise potentially undetected by the systems mentioned above. Choose the solution that best fit your company

Read the analysis
·Emerging Threats

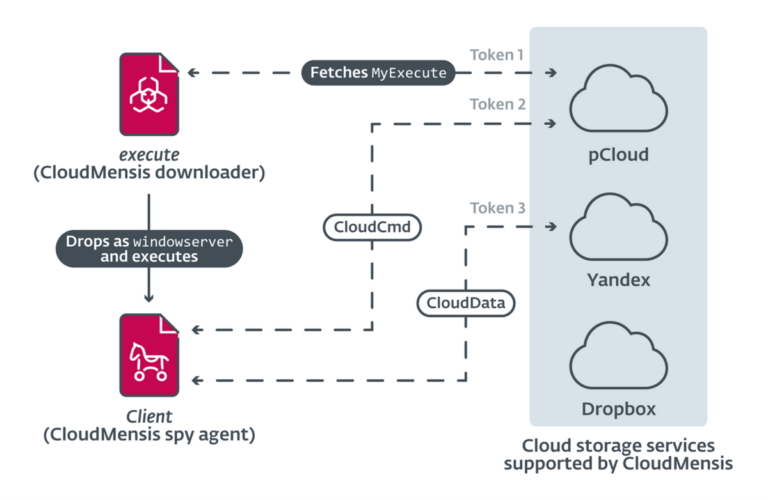
CloudMensis: Spyware hitting MacOS

A new backdoor for MacOS systems has been discovered in recent days by ESET researchers. The goal of the malware is to exfiltrate information from the victim system by exploiting cloud storage services.The Backdoor, named by CloudMensis researchers, recovers information such as documents, email messages and attachments, files on removable devices, screenshots and the sequence … Read more

Read the analysis
·Emerging Threats

Raspberry Robin: How to defend

In May 2022, a new, particularly evasive Worm was observed for the first time, spreading in private and corporate networks through compromised USB sticks.This new Worm has been given the name “Raspberry Robin“. Worms that propagate through USB devices are certainly not new threats and very often, since they are old malware, command and control … Read more

Read the analysis
·Featured

What happens during a Ransomware Attack?

The Incident Response activities carried out by our Team in the last period confirm the growing trend in the number of cyber attacks against Italian companies. What should make us reflect (beyond the numbers and the damage caused) is the technical evolution and increase in complexity of the latter. In fact, we notice greater interaction … Read more

Read the analysis
·Malware Analysis

Agent Tesla Reverse Engineering

On January 24, 2023, Fortgale identified an Agent Tesla malware campaign being delivered via email to compromise the systems of Italian companies. In this technical article, we will analyze the behavior of the malware and how it compromised its victims through the analysis of code characteristics and collected data. It has now become common practice … Read more

Read the analysis
·Malware Analysis

Server VMware ESXi – Ransomware Attacks in Italy

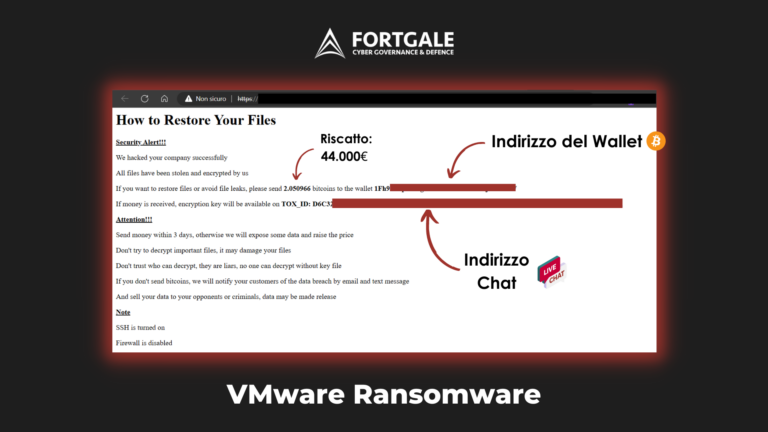
VMware ESXi  #Ransomware: What is going on? What does the following code means? D6C324719AD0AA50A54E4F8DED8E8220D8698DD67B218B5429466C40E7F72657C015D86C7E4A In the last few hours, several sources have reported massive Ransomware-type activity against VMware ESXi servers exposed on a public network. The activity currently appears to be conducted by at least 2 different criminal groups. How? Both groups are exploiting a … Read more

Read the analysis
·Defence

HTML Smuggling and IceID Trojan: A Guide to Corporate Defense

In March, Fortgale detected a significant increase in malicious activity targeting Italian companies associated with the spread of the Trojan IceID malware. The most relevant activity was identified in the March 16 campaign in which the criminal actor manipulated previous conversations of the victims by inserting a malicious attachment with theHTML Smuggling technique: A company … Read more

Read the analysis
Blog home