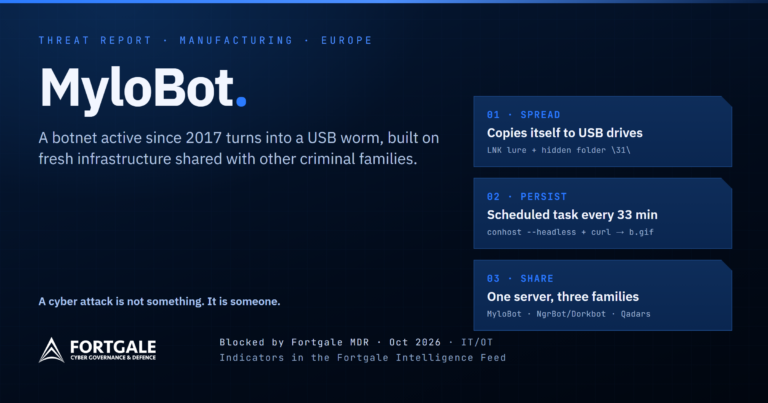
MyloBot goes USB: the botnet that crawls towards the production line
Fortgale MDR stopped a new MyloBot variant at a European manufacturing company: the botnet now spreads as a USB worm, on fresh infrastructure shared with NgrBot/Dorkbot and Qadars.
Tag
Fortgale MDR stopped a new MyloBot variant at a European manufacturing company: the botnet now spreads as a USB worm, on fresh infrastructure shared with NgrBot/Dorkbot and Qadars.
In 2021, Fortgale conducted an Incident Response operation to eradicate the WannaMine malware from the systems of an Italian company operating in the industrial sector. The malware proliferated across several hundred systems, exploiting a variety of propagation techniques. Upon installation, WannaMine initiates cryptocurrency mining activities, leading to substantial disruptions in the company’s operations due to … Read more
WannaMine cryptominer worm: lateral movement via EternalBlue, Mimikatz credential harvesting, persistence mechanisms and the field intervention to remediate a long-running compromise.
PurpleFox malware framework: rootkit components, MSI installer abuse, exploit-driven worm capabilities and lateral movement patterns observed in Italian intrusions.