Stylesmuggler magento 0day
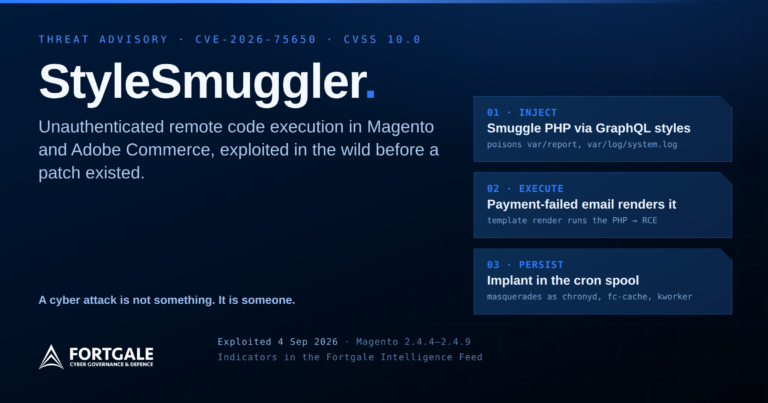
On 4 September 2026 at 22:20 UTC, an unauthenticated request began landing on Magento and Adobe Commerce storefronts and walking straight to remote code execution. No login. No admin session. No plugin. The flaw, tracked as CVE-2026-75650 and named StyleSmuggler, carries a CVSS of 10.0, and it was exploited in the wild for roughly three … Read more
