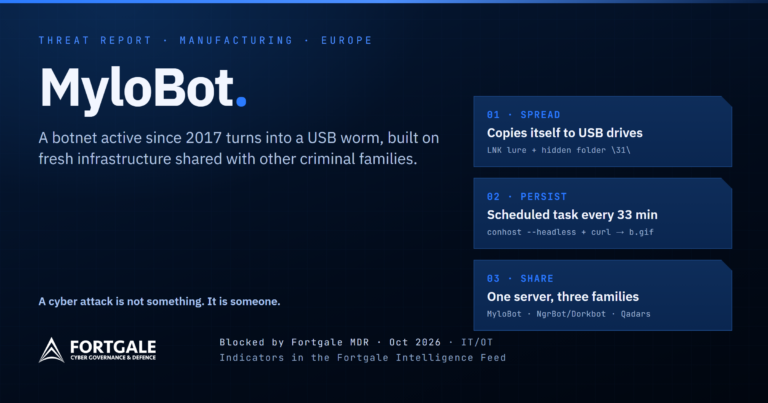
MyloBot goes USB: the botnet that crawls towards the production line
Fortgale MDR stopped a new MyloBot variant at a European manufacturing company: the botnet now spreads as a USB worm, on fresh infrastructure shared with NgrBot/Dorkbot and Qadars.
Someone you can track, analyse, anticipate.
Need a hand? See how Fortgale can help — our services and support.
Blog · research & analysis
Fortgale MDR stopped a new MyloBot variant at a European manufacturing company: the botnet now spreads as a USB worm, on fresh infrastructure shared with NgrBot/Dorkbot and Qadars.
On 4 September 2026 at 22:20 UTC, an unauthenticated request began landing on Magento and Adobe Commerce storefronts and walking straight to remote code execution. No login. No admin session. No plugin. The flaw, tracked as CVE-2026-75650 and named StyleSmuggler, carries a CVSS of 10.0, and it was exploited in the wild for roughly three … Read more
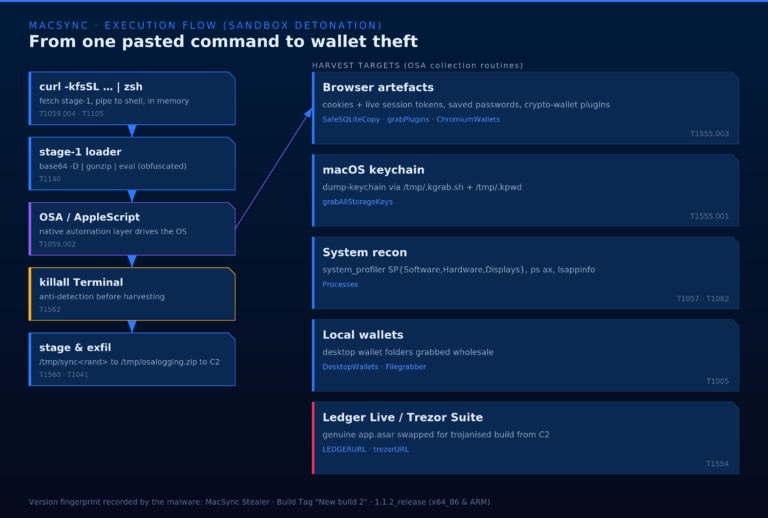
No exploit. No attachment. No phishing email. In this campaign the threat actor needs the victim to do exactly one thing: copy a command from an installation guide and paste it into the macOS Terminal. In the summer of 2026 our SOC intercepted that moment three times, on the same corporate endpoint, and blocked it three times. The target: a developer’s Mac. The payload: MacSync, an infostealer sold as Malware-as-a-Service and built for the Apple ecosystem
ABSTRACT The FBI recently issued an advisory on Kali365, a Phishing-as-a-Service platform that abuses legitimate Microsoft OAuth flows to bypass multi-factor authentication. Kali365 is a Phishing-as-a-Service platform that bypasses Microsoft MFA by abusing the OAuth Device Code Flow. For $250, an operator with minimal skill acquires enterprise-grade identity compromise capability. The technique does not break … Read more
Intelligence · Phishing Kit · Q1 2026 April 24, 2026Fortgale CTI14 min readRPT-26-0424 Observation of the quarter The 2026 phishing ecosystem has outpaced traditional defenses. MFA alone is not enough. The answer is not one more product but a managed defense that combines phishing-resistant authentication, session-level detection, intelligence-driven and AI triage. An attack is not … Read more
In the high-stakes world of venture capital and corporate funding, where millions hang in the balance and sensitive financial data flows freely, a new breed of cyber threat is emerging. Imagine receiving an email that looks like a golden opportunity—a potential investor reaching out just as your company navigates a critical funding round. It’s polished, … Read more
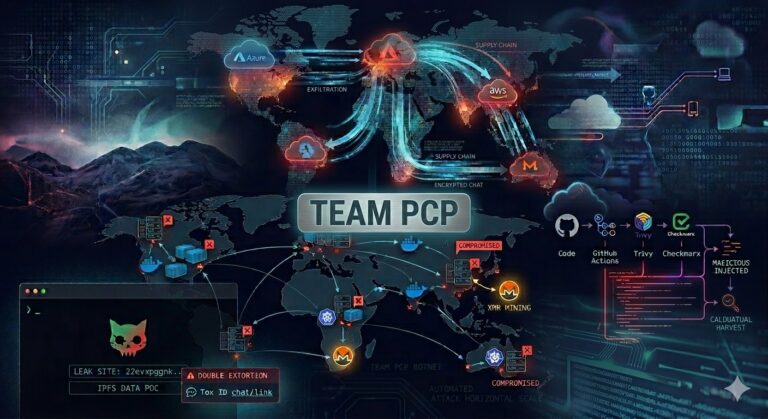
TeamPCP: The Rise of Cloud-Native Extortion and Supply Chain Attacks TeamPCP is an emerging cybercriminal collective that became active in late 2025, distinguishing itself through a specialized focus on massive attacks against cloud-native infrastructures. Unlike traditional Advanced Persistent Threat (APT) groups that often prioritize deep persistence on specific endpoints, TeamPCP utilizes high-level automation to scale … Read more
In February 2026, the Fortgale Incident Response team investigated a multi-stage intrusion attributed to Mora_001, a Russian-origin threat actor exploiting Fortinet vulnerabilities. The campaign, internally dubbed “FortiSync Quasar,” revealed an evolution from ransomware operations to strategic espionage, deploying Matanbuchus 3.0, Astarion RAT, and SystemBC. Rapid containment prevented any data exfiltration.
The Microsoft 365 environment ranks among the primary platforms targeted by threat actors. By its very nature, it is exposed to a wide spectrum of offensive operations — and precisely for this reason, Microsoft continuously introduces new tools and configurations to help organizations cope with this ever-shifting landscape of attacks (such as Conditional Access policies … Read more