


01 ·
Integrated Cyber Threat Intelligence
Real expertise on threats, not a help desk.
And someone can be known, anticipated, stopped.
Fortgale is a European cybersecurity company specialised in defence against advanced threats. Our SOC in Milan, operating 24·7·365 with senior analysts, detects and contains attacks within measurable timeframes; the Cyber Threat Intelligence produced by our analysts tracks the offensive groups targeting European organisations and gives weight to every alert.
Median containment in <30 minutes from confirmed alert. The service integrates with the technologies the organisation already uses and strengthens them, with no vendor lock-in.
NIS2 and DORA compliant.

Fortgale was founded in Milan in 2017 with a focus on Cyber Defence and Governance. Our Competence Center specialises in malware analysis, Cyber Threat Intelligence, Incident Response and Threat Hunting, and every day turns this expertise into operational knowledge and continuity for our clients.
From the SOC in Milan, operating 24·7·365, our senior analysts work across multiple security technologies. Fortgale protects organisations in 11 strategic sectors, including manufacturing and automotive, banking, finance and insurance, aerospace and defence, aviation and maritime transport, and serves clients in 22 countries across EMEA, America and APAC. Cyber Defence, Cyber Threat Intelligence and Advisory converge in the Fortgale Defence Platform.
Four integrated services: SOC and MDR defend the corporate infrastructure, Cyber Threat Intelligence strengthens the defence and supports the decisions of the board, Advisory consolidates the defensive posture and regulatory compliance. A single point of contact protects the organisation before, during and after the attack.
Defence of the corporate infrastructure from our SOC in Milan, operating 24·7·365 with senior analysts. Triage, escalation and incident management within the European regulatory context.
Managed detection and response across endpoint, identity, cloud and network, driven by threat intelligence. Median detection <15 min, containment <30 min.
Defensive enhancement to counter, prevent and understand digital threats: up-to-date profiles of 287 hostile tools and actors active across European markets and strategic support for the board.
Specialist consulting to consolidate the defensive posture and support regulatory compliance: risk assessment, NIS2 and DORA, tabletop exercises on real scenarios, vCISO.
The Fortgale Defence Platform provides centralised access to all security information: threat management, incident register and Cyber Threat Intelligence sharing.
Real expertise on threats, not a help desk.
Experience in handling complex incidents conducted by advanced threat actors.
Full autonomy in eradicating the attacker from corporate systems and networks.
Fortgale adapts to the technologies the client already uses and strengthens them.
Independent of the technologies in place.
Maximum effectiveness in threat management.
Our analysts study the threats active against European organisations: they profile the actors, analyse the malware, reconstruct the campaigns. This research feeds the detection and response of our services and is regularly cited by institutions, leading companies and specialist cybersecurity media. We don't aggregate third-party feeds, we publish only what we have verified first-hand.
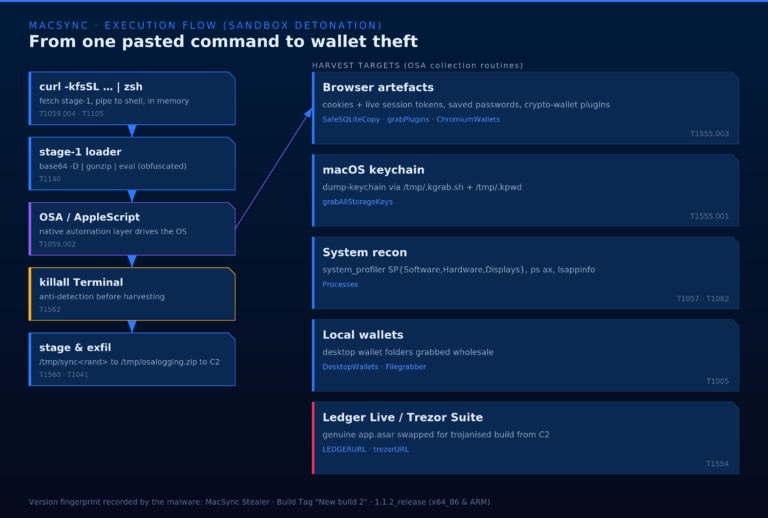
No exploit. No attachment. No phishing email. In this campaign the threat actor needs the victim to do exactly one thing: copy a command from an installation guide and paste it i…
Read article →
ABSTRACT The FBI recently issued an advisory on Kali365, a Phishing-as-a-Service platform that abuses legitimate Microsoft OAuth flows to bypass multi-factor authentication. Kali…
Read article →
Intelligence · Phishing Kit · Q1 2026 April 24, 2026Fortgale CTI14 min readRPT-26-0424 Observation of the quarter The 2026 phishing ecosystem has outpaced traditional defenses. M…
Read article →
In the high-stakes world of venture capital and corporate funding, where millions hang in the balance and sensitive financial data flows freely, a new breed of cyber threat is em…
Read article →
In February 2026, the Fortgale Incident Response team investigated a multi-stage intrusion attributed to Mora_001, a Russian-origin threat actor exploiting Fortinet vulnerabiliti…
Read article →
UPDATES: 27.11.2024: As mentioned by TrustWave, "Supercar Phishing Kit" has an high level of overlapping with the most recent update of "Rockstar 2FA Phishing-as-a-Service" 26.09…
Read article →Cited by The Hacker News · Google Cloud Blog · GData · HiSolutions Research · Cybersecurity Trends · Tom's Hardware · All references
Resources: cybersecurity guides and glossary → · Incident Response 24·7 →
A meeting protected by a non-disclosure agreement and a technical conversation with our senior analysts. Within 72 hours of the meeting you will receive the Report on your sector.
No nurturing sequences, no auto-replies. One of our analysts calls you back within one business day.
The full Report (executive summary · operational IoCs · technical runbook) is restricted. Share two details and one of our analysts contacts you with access and a short technical briefing.
Response in 30 minutes, containment in 1–4 hours. Even if you are not a Fortgale customer.